Sonar overview
SonarSource is a leading software development company focused on helping organizations write clean, secure, reliable, and maintainable code. Its flagship platform, SonarQube, provides automated code analysis that identifies bugs, vulnerabilities, security hotspots, code smells, and technical debt across multiple programming languages. SonarSource integrates directly into developers’ workflows and CI/CD pipelines, enabling teams to detect and resolve code quality issues early in the software development lifecycle.
The platform supports continuous inspection, giving development teams real-time visibility into code health and helping organizations establish consistent quality standards. SonarSource’s solutions are designed for developers, engineering teams, and enterprises seeking to improve software quality without slowing delivery.
By combining static analysis, security checks, quality gates, and actionable remediation guidance, SonarSource helps organizations reduce technical debt, strengthen application security, and deliver more trustworthy software. Its tools integrate with popular development environments, source-control platforms, and DevOps technologies, making code quality an integral part of modern software development.
Media
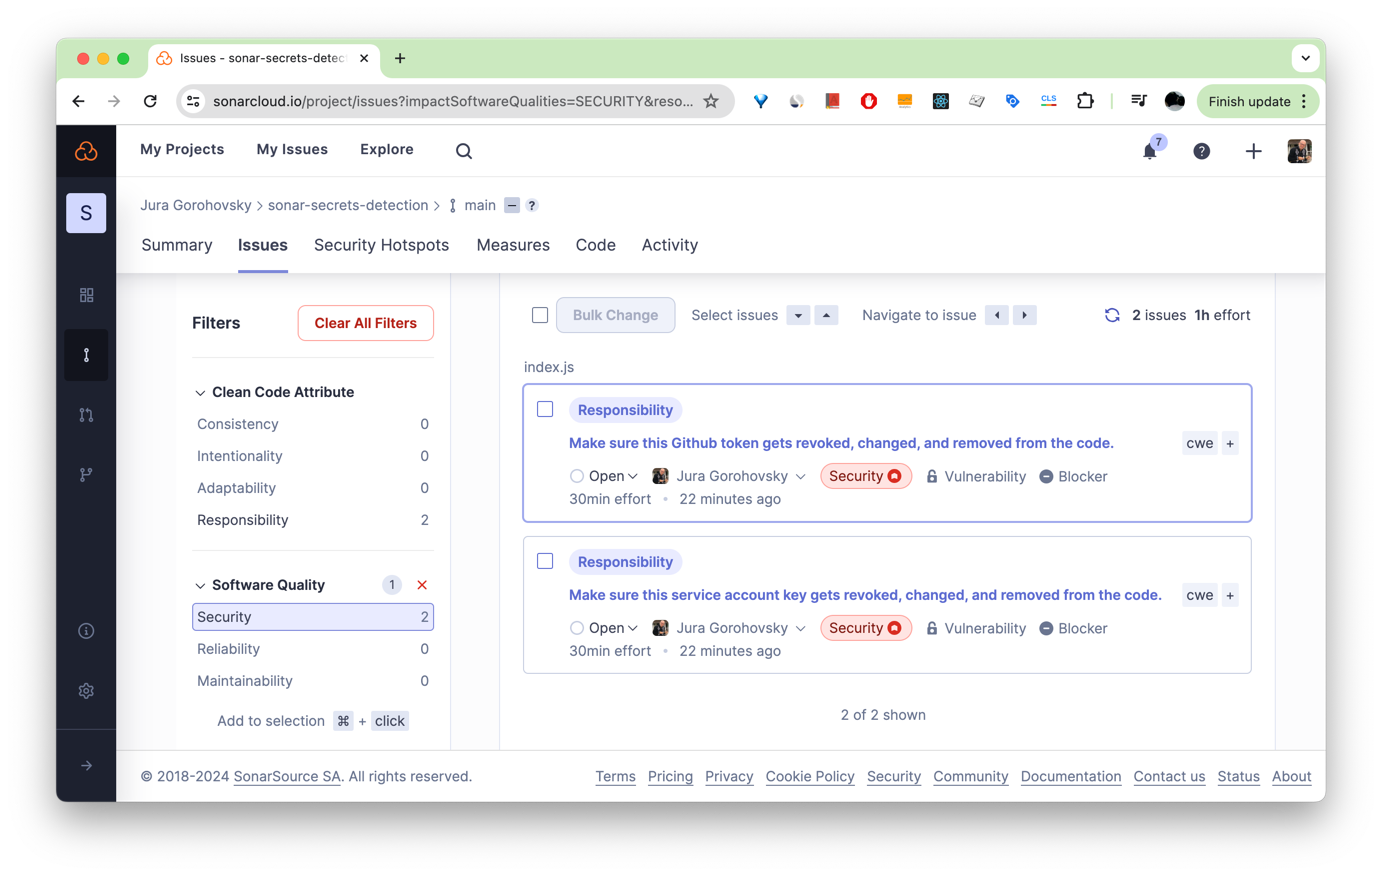
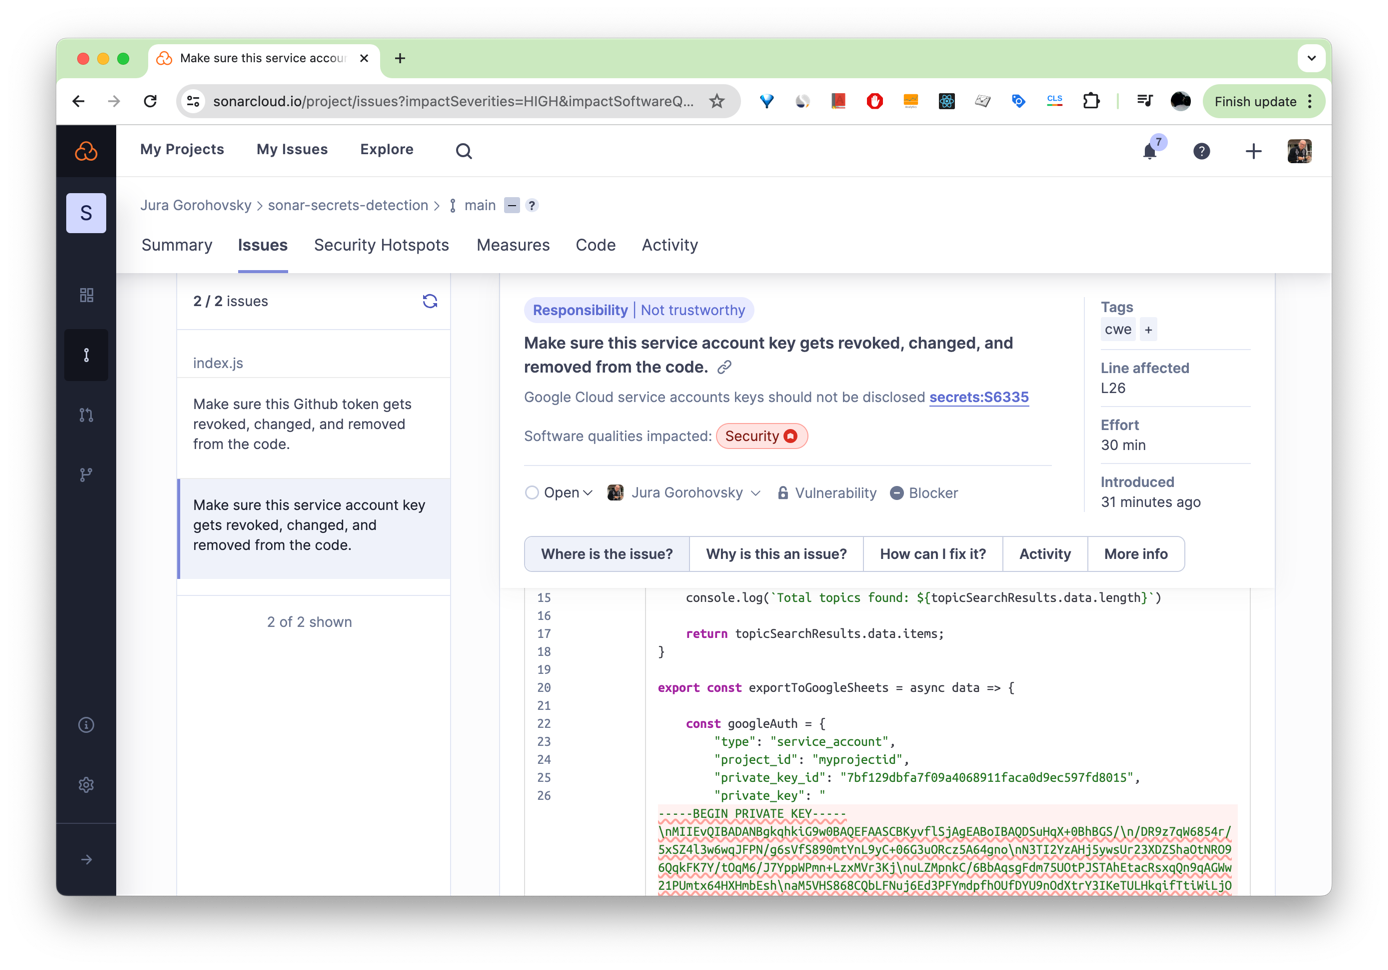
Screenshots and product photos shared by SonarSource SA.
Company Information
 Geneva, Switzerland (US: Austin, Texas)

VisionA world where all code — human- and AI-written — is clean, safe and reliable by default — where every developer gets instant feedback that keeps quality and security high before code ever ships.

MissionWe build code-quality and code-security tools, so development teams detect and fix bugs, vulnerabilities and quality issues in their code — including AI-generated code — continuously and early.
Leadership team
Meet the leaders shaping our vision, product, and growth.
No leadership team has been added for this product yet.
Pricing
All plans include core features. Per month, billed annually.
Features
All capabilities grouped by category.
- Static analysis (SAST)
- Bug and vulnerability detection
- Code smell and quality detection
- Multi-language support
- Security hotspots
- Quality gates in CI/CD
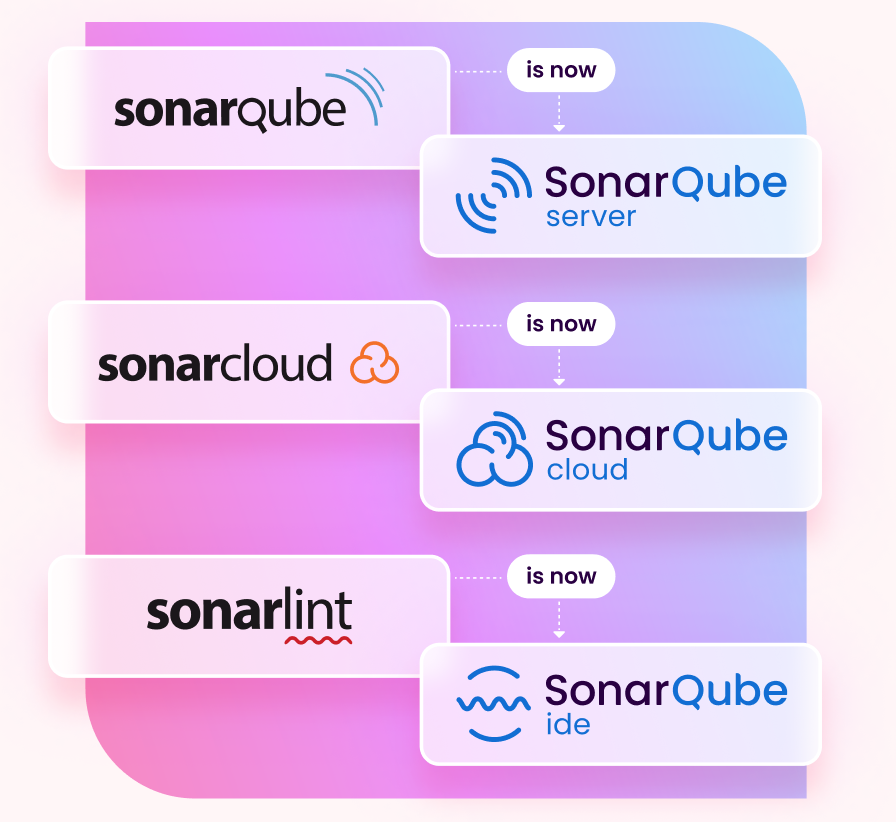
- In-IDE feedback (SonarLint)
- Pull-request analysis
- AI-code assurance
- Coverage and duplication
- SonarQube Server (self-managed)
- SonarQube Cloud (SaaS)
- Community/Developer/Enterprise editions
- Integrations across the stack
- APIs

 Recommended for teams <50 developers